 50.8k
- ClickHouse Security

The agentic SIEM built for scale
Collect, detect, and investigate in one platform, on the database built for large-volume, high-speed workloads. Then build agentic workflows on the same data.
Now in private preview
- Hundreds of first-party integrations, ready to query on arrival
- Native pipelines, no third-party tools required
- Built-in, managed detections, plus custom SQL and Sigma rules
- MCP server, AI chat, Slack bot, CLI, and API access
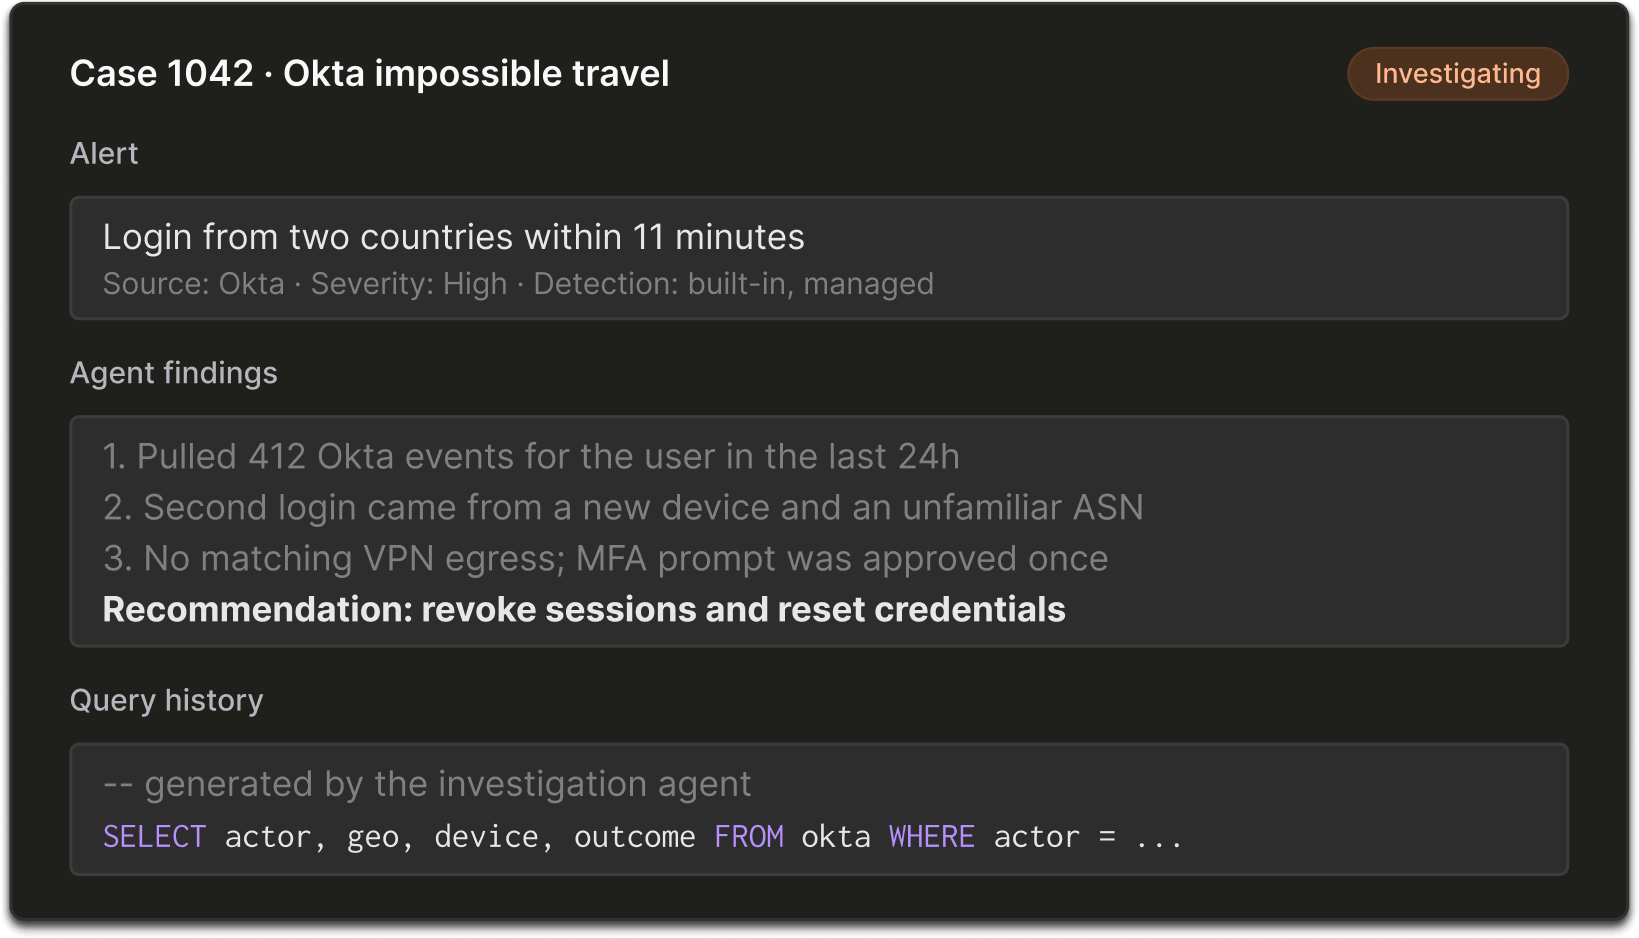
Start with a SIEM that has the essentials built in. Then use AI to keep pace with modern threats.
Foundational data management
- Hundreds of first-party integrations, normalized and ready to query on arrival
- Filter, route, and drop data with built-in pipelines
- Managed and custom SQL detections-as-code
Flexibility to build in the AI era
- Native AI agent that automatically triages and investigates alerts
- Bring-your-own-LLM support
- Leverage your data from the MCP server, native AI chat, Slack bot, CLI, or API
From raw logs to resolved cases
Build and run agents that use your security data to solve real problems
Agents triage and investigate your alerts out of the box. Build your own to handle response, threat hunting, and detection coverage.

Autonomous triage
Alerts automatically trigger agents to gather context and investigate incidents.

Chat with your agent in app or Slack
Ask questions of your logs in natural language, wherever your team works.

Transparent and governed
See which logs were analyzed and why. Control models and permissions per agent.

AI detection engineering
Generate rules from descriptions, audit coverage, and tune noisy detections.
Why ClickHouse Security
- No
3+ hours of manual log correlation
- No
Custom rules written for every threat
- No
Weeks or months integrating sources
- No
Hand-built pipelines per log source
- No
Separate SIEM, pipeline, and AI SOC vendors
- Yes
AI gathers context and correlates events, cutting investigations to minutes
- Yes
Built-in library covers common threats with the option for custom SQL and Sigma detections
- Yes
Connect sources and start detecting quickly
- Yes
Built-in filtering, routing, enrichment, and normalization
- Yes
One platform for ingestion through AI investigations
Request access to ClickHouse Security
See the full platform on your own data. We’ll get you started with a trial or a guided demo.